Why You Should Make Adopting Current Long-Life Releases a Habit
Hey everyone — At Pure Storage, we see many customers who still think about storage upgrades like old-school firmware: “set it and forget it” until it’s forced to change. But FlashArray isn’t firmware it’s modern, continually improved, and designed for an agile, secure, predictable data platform. That means it’s time to make adopting recent Long-Life Releases (LLRs) a regular habit not just something you reluctantly do, "when you have to". LLRs should be your standard practice: ✅ Fresh Features, Mature Code Each LLR is built on code that’s been running in production for at least 8 months before it branches. That means you get the innovations from recent Feature Releases — tested, stabilized, and production-proven. You avoid missing out on valuable improvements while still benefiting from enterprise-grade predictability. ✅ Consistent Security and Compliance Aging too far behind, even on an LLR, can expose you to security vulnerabilities and unsupported configurations. By habitually adopting recent LLRs, you ensure you’re in the supported window for critical patches and compliance audits and avoiding fire drills later. ✅ Reduce Technical Debt Getting stuck on very old LLRs can build up technical debt. Skipping multiple versions makes your next upgrade harder, riskier, and more time-consuming. Keeping up with recent LLRs means smoother transitions, less operational friction, and easier adoption of the next improvements. ✅ Keep Innovation Flowing The idea that an LLR is “old code” is a myth. Recent LLRs contain carefully chosen, well-hardened feature improvements. If you wait too long, you lock yourself out of meaningful performance, efficiency, and capability gains that your peers are already using. ✅ Break the Firmware Mentality FlashArray is software-driven, and has a rapid but reliable development model. Treating it like outdated firmware, and you miss the true value. The LLR program is designed precisely to let you safely adopt modern features and maintain enterprise-grade stability and maintain a predictable cadence. Bottom line? Adopting recent Long-Life Releases, habitually, is the best way to get modern features, maintain security, reduce upgrade risk, and keep your environment aligned with Pure’s best practices. You deserve innovation and peace of mind. Don’t settle for less by sticking with outdated code. If you want help reviewing which LLR is right for you, or understanding the timelines, just reach out — we’re here to help you stay current, secure, and ahead of the game.1.3KViews8likes2Comments
ActiveCluster for File
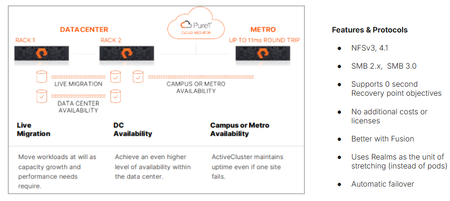
We’re proud to announce the availability of ActiveCluster for file, Everpure’s premier business continuity solution and a fundamental enabler of our Enterprise Data Cloud vision, where Service Level Agreements define what storage, network and compute resources are assigned dynamically to application data sets rather than an hardware-to-app architectures. With ActiveCluster for file, Everpure is extending the benefits of data mobility, continuous access and policy-driven management to file workloads. What is ActiveCluster? Everpure launched ActiveCluster in 2017, and rapidly took the mission critical, enterprise block storage world by storm. ActiveCluster rapidly enabled enterprise customers with the most demanding block workloads to deploy synchronous, always available, always up-to-date, LUNs or volumes to hosts stretched across geographic distances. What set ActiveCluster apart from the existing solutions at the time, and even now, is how simple to set up Everpure RTO-0 and RPO-0 file solutions are, and how flexible and adaptable to the ever changing business needs hosting these data sets become after being deployed on a Everpure Fusion fleets. Today, we’re adding file protocol support like NFSv3, NFSv4.1, SMB 2.0, and SMB 3.0 w/ continuously available shares to our ActiveCluster solution. Realms as a new container ActiveCluster for file utilizes a new, high-level container called a Realm, to synchronously mirror both user data and storage configuration information necessary to provide data access to authorized users on either side of the stretched file system(s). Realms are handy to put applications with similar Recovery Point Objectives and similar Recovery Time Objectives together. Realm Synchronous Replication The act of synchronously mirroring both the user data and storage configuration information across two different FlashArrays is called ‘stretching’. Similar to how a pod is stretched across two FlashArrays, a Realm can be stretched between any FlashArray system that has no more than 11ms Round Trip Time average latencies on their array replication links. Either Fibrechannel or Ethernet array replication links can be used to replicate file data synchronously. Figure 1. ActiveCluster for file can be deployed in different modalities Realms as namespaces for policies Realms contain unique snapshot, audit logging, replication and export policies. These policies are only viewable and attachable to storage objects within the Realm, creating a building block for hosting multiple different end customers or tenants on Fusion fleets. These policies are automatically replicated over to the other array if the Realm is stretched, reducing operator burden in failover scenarios. To prevent split brain scenarios (where a network partition in the array links or replication links stop communication between the pair of FlashArrays) Everpure’s fully managed Cloud Mediator service will determine which remaining FlashArray controller pair can process writes, and which array will not. Unlike other business continuity solutions, ActiveCluster customers don’t have to worry about patching or maintaining the security of separate VMs to act as a mediator service to prevent split brain scenarios. Multiple servers supported per Realm, different IDPs allowed. Each Realm can have one or more servers configured in it, which act as protocol end points for clients and hosts to connect to. Each server in a Realm can have a different IP address, or utilize a different Identity Provider Service. When a failover condition occurs (like a site disaster on one side), automatic failover and the clients in either data center are on the same Ethernet segment or broadcast domain, a failover condition will emit a gratuitous Reverse Address Resolution Protocol request (RARP), mapping the new MAC address of the ethernet interface on one side to a same IP address being used. Applications may see a small pause in reads or writes being serviced, but will not have to re-issue I/O or remount / remap shares or exports. Managed directory quotas can also be used for any filesystem or managed directory attached to the servers in the Realm being stretched. These quota policies automatically get replicated with user data, so the same customer experience in terms of usable space exists both before and after an automatic failover. New Guided Setup available for ActiveCluster for file Deploying new ActiveCluster for file solutions can occur in less than five minutes on already racked and powered arrays. A Guided Setup wizard is available to quickly capture the necessary information to stretch a Realm. This wizard can be started from multiple locations within the Purity GUI. ActiveCluster for file fully takes advantage of Fusion fleets and the ability to manage storage infrastructure as code, programmatically and via policy. Realms are not tied to hardware, and can ‘float’ Realms with ActiveCluster for file support not only provide a 0-RTO and 0-Recovery Point Object at the storage layer for mission critical applications, but they also provide a mechanism to transparently move the data and configuration in the Realm non-disruptively somewhere else within your fleet, whether it’s follow the Sun type round-robin hops, where the Realm’s location changes depending on the time of day, or is moved as a part of a data-center migration. Coupled with Fusion, Everpure’s intelligent control plane, ActiveCluster for file enables workloads and application data and their configuration information to dynamically and seamlessly move to the right location, at the right time, at the right granularity. Seamless movement across greater geographic distances can be accomplished by stretching and unstretching the same Realm between different arrays, as long as the RTT latency between them is <11ms. Service Level Agreements are the lingua franca of the Enterprise Data Cloud Service Level Agreements are the natural language of business owners, and are integral for companies who want to move away from managing storage arrays to managing their business data. They capture answers to questions like “How fast do you need access to this data? Does it need to be backed up or otherwise protected against site-wide failure? SLAs are what forms our vision behind the App-to-data operational model. This App-to-data model takes abstract, high level business requirements as input, and then automatically configures and deploys the required storage services to meet the service level agreement just defined. A Fusion fleet manager’s perspective is one of many different application tiles, and their health, not just a series of HA pairs spread out across different data centers. Data management operations, like instant backups, cloning, movement is applied as “verbs” to the application data set’s name or workload ID, and not to a mismatched storage container whose hardware boundaries impose limits on your app team. An Intelligent, unified control plane manages and enforces SLA’s across the fleet autonomously, like a modern cloud operating model but that can be deployed in any modality, whether on-prem, in the cloud or a hybrid. This scalable model, with Fusion’s intelligent control plane, supports ALL workloads, from modern AI workloads, containers and High Performance Workloads to extremely large image or rich media archives. An Enterprise Data Cloud, made up of discrete nodes tied loosely together, where Service Level Definitions define autonomous system behavior. Stop managing your storage arrays, and start managing your data. Learn more about ActiveCluster for file Read the support documentation for Purity 6.12.0 Test and deploy Fusion fleets and file presets Ask your account executive or system engineer for a demo!1.5KViews5likes0CommentsEntra ID SAML2 SSO on FlashArray (Purity//FA 6.12.3), including fleets
Hi everyone, Here is a working setup for single sign-on from Microsoft Entra ID to a FlashArray, tested on Purity//FA 6.12.3, which is the newest version at the time of writing. It follows the Microsoft tutorial for Pure Storage SSO (https://learn.microsoft.com/en-us/entra/identity/saas-apps/pure-storage-sso-tutorial) and adds the fixes I needed to get the login test to pass. It also covers adding more arrays and fleets. Two things that break the login if you skip them The gallery app ships with role names that do not match the FlashArray role names. If you do not rename them, the login test fails because the array cannot find the role (Step 6). The claims must have no namespace URI (Step 5). What you need An array admin login Entra admin rights (Enterprise applications and App registrations) The Pure Storage SSO app from the Entra App Gallery A user or group to assign Overview Create a certificate on the array Configure SAML2 SSO on the array Entra app and the array certificate Load the Entra signing certificate on the array Claims (delete the namespace URI) Fix the app role names Assign, test and enable Plus: more arrays and fleets, and a troubleshooting list at the end. Step 1: Create a certificate on the array The array needs its own RSA certificate to sign SAML requests and decrypt assertions. Do not use the management certificate: it is EC 256 and caused a 500 error for me. purecert self-signed create saml-sp --common-name myarray.pure --days 365 purecert list The saml-sp row should show self-signed, rsa, 2048. Note the expiry date: SSO signing stops working when it expires. Step 2: Configure SAML2 SSO on the array Go to Settings › Access › Users and Policies › SAML2 SSO and edit the configuration. Array URL: the array FQDN, for example https://myarray.pure/. Signing Credential and Decryption Credential: type the certificate name saml-sp. Do not paste certificate text. Switch on Sign Request and Encrypt Assertion. IdP Entity ID, URL and IdP Metadata URL: copy them from the Entra app (Set up Pure Storage SSO section). Keep Enabled off for now and save. Without credentials, saving fails with "Must provide signing credential when signed request is enabled" and the same message for decryption. The GUI can silently keep management, so check the result in the CLI: puresso saml2 list puresso saml2 test Both credential columns must show saml-sp. If not, set them directly: puresso saml2 setattr Entra-ID --signing-credential saml-sp --decryption-credential saml-sp This can print "Certificate claim does not exist." even though the values were applied, so trust the list output. Step 3: Entra app and the array certificate In the Entra admin center go to Enterprise apps › New application, search Pure Storage SSO and add it. Open Single sign-on › SAML › Basic SAML Configuration. Set Identifier to the array's SP Entity ID and Reply URL to the array's Assertion Consumer URL. Both are shown in the array's SAML2 SSO dialog, so copy them from there. On the array, open the certificates page and download saml-sp. Rename the extension from .crt to .cer. In the Entra app go to Single sign-on › SAML Certificates › Verification certificates › Edit, tick Require verification certificates, and upload the .cer. Because Encrypt Assertion is on, also import the same .cer under Token encryption and activate it (see the token encryption guide under Links). Check that you exported the right certificate: openssl x509 -in saml-sp.cer -noout -subject -enddate The subject must show the common name you used in Step 1, not the GUI certificate. Step 4: Load the Entra signing certificate on the array The array needs Entra's signing certificate to validate the response. If this is empty the array test still shows OK, but a real login fails. In Entra open Single sign-on › SAML Certificates and download Certificate (Base64). Open the file, copy everything including the BEGIN CERTIFICATE and END CERTIFICATE lines. In the array's SAML2 SSO dialog click Edit next to Verification Certificate and paste it. CLI alternative: puresso saml2 setattr Entra-ID --verification-certificate Step 5: Claims (delete the namespace URI) In the Entra app go to Single sign-on › Attributes & Claims › Edit. Open each claim, clear the Namespace field completely, and make sure the names match exactly: dn: user.onpremisesdistinguishedname email: user.mail (or user.userprincipalname for UPN) family_name: user.surname given_name: user.givenname purity_roles: user.assignedroles (required for array level SSO) Step 6: Fix the app role names The Pure Storage SSO gallery app is set up incorrectly for its role names. It ships readonly_role, ops_admin_role, storage_admin_role and array_admin_role with an empty value. The names must match the FlashArray role names exactly, otherwise the login test fails because the array cannot find the role. The roles are edited in App registrations, not in the Enterprise application: Go to App registrations › All applications and search for the app name. Open App roles and click a role. In Display name, remove the _role suffix. In Value, enter the role name, for example array_admin. Click Apply and repeat for the other roles. array_admin_role → Display name: array_admin, Value: array_admin storage_admin_role → Display name: storage_admin, Value: storage_admin ops_admin_role → Display name: ops_admin, Value: ops_admin readonly_role → Display name: readonly, Value: readonly Leave msiam_access as it is. Step 7: Assign, test and enable In the Entra app go to Users and groups › Add user/group, pick the user, click Select a role and choose one of the renamed roles. Only one role per assignment. On the array open the SAML2 SSO dialog and click Test. All lines must be green and the first two must show saml-sp. Click E2E Test, sign in with the assigned user, then click Check E2E Test Result. If it passes, switch Enabled on and save. The login page now shows Click for Single Sign-On and a Local Access link. Tip: Keep a working local admin login in case something on the Entra side breaks or a certificate expires. More arrays and fleets Each array needs its own certificate, and that certificate must be uploaded to Entra under Verification certificates, next to the ones from the other arrays. You do not need a new Enterprise application per array. If you use Fusion / fleet manager, enable Trust Other SAML Service Providers In Fleet in the SAML2 SSO configuration and apply these settings on each additional array: Create the certificate on that array (Step 1) with its own common name. Use the same SSO configuration name as on the first array. Array URL: the FQDN of the new array. SP Entity ID: set it to Manual and paste the SP Entity ID of the first array. All fleet members must use the same SP Entity ID. Signing Credential and Decryption Credential: saml-sp, the certificate of this array. Switch on Sign Request and Encrypt Assertion. Identity Provider fields and Verification Certificate: the same values you used on the first array. In the Entra app, add a second Reply URL with the Assertion Consumer URL of the new array, and upload the new array's saml-sp .cer under Verification certificates. Run Test and E2E Test before enabling. After that you can sign in on the other arrays with the same Entra users, roles and claims. Note: If you use Encrypt Assertion on several arrays, check this: Entra token encryption uses one active certificate per application, so test each array with the E2E test. Troubleshooting Save fails: must provide signing or decryption credential: Create saml-sp and enter its name in both fields Red error echoes a long MIID... string: You pasted certificate text. Type the certificate name instead Test shows management as credential: Run puresso saml2 setattr as in Step 2 500 Internal Server Error when starting login: The credential was the EC management certificate. Switch to the RSA saml-sp certificate Login test fails, role not found: Rename role display name and value in App registrations (Step 6) Login fails or user has no role: Clear the claim namespaces and check purity_roles = user.assignedroles (Step 5) Verification certificate shows - in the test: Paste the Entra Base64 certificate (Step 4) If you do not need signed requests or encrypted assertions, you can switch off Sign Request and Encrypt Assertion and skip the certificate steps. Links Configure Pure Storage SSO for Single sign-on with Microsoft Entra ID (https://learn.microsoft.com/en-us/entra/identity/saas-apps/pure-storage-sso-tutorial) Configure Microsoft Entra SAML token encryption (https://learn.microsoft.com/en-us/entra/identity/enterprise-apps/howto-saml-token-encryption) Manage certificates for federated single sign-on (https://learn.microsoft.com/en-us/entra/identity/enterprise-apps/tutorial-manage-certificates-for-federated-single-sign-on) App roles UI (https://learn.microsoft.com/en-us/entra/identity-platform/howto-add-app-roles-in-apps#app-roles-ui) Hope this saves someone some time. Questions and corrections are welcome.81Views4likes0Comments
Backup and Restore FA Configuration
Hi All, Purestorage has how to save or backup and restore configuration when an issue occurs? For example, the software crashed and could not be used anymore. Once the problem was fixed, we restored the existing configuration file from backup.Solved1.6KViews4likes6CommentsFlash Array Certification
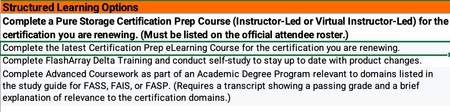
All FlashArray Admins, If any of you currently hold a Flash Array certification there is an alternative to retaking the test to renew your cert. The Continuing Pure Education (CPE) program takes into account learning activities and community engagement and contribution hours to renew your FA certification. I just successfully renewed my Flash Array Storage Professional cert by tracking my activities. Below are the details I received from Pure. Customers can earn 1 CPE credit per hour of session attendance at Accelerate, for a maximum of 10 CPEs total (i.e., up to 10 hours of sessions). Sessions must be attended live. I would go ahead and add all the sessions you attended at Accelerate to the CPE_Submission form. Associate-level certifications will auto-renew as long as there is at least one active higher-level certification (e.g., Data Storage Associate will auto-renew anytime a Professional-level cert is renewed). All certifications other than the Data Storage Associate should be renewed separately. At this time, the CPE program only applies to FlashArray-based exams. Non- FA exams may be renewed by retaking the respective test every three years. You should be able to get the CPE submission form from your account team. Once complete email your recertification Log to [email protected] for formal processing. -Charlie363Views3likes0CommentsChoosing Between Snapshots and Backups? Use Both
Let's settle the old debate: snapshots or backups for data protection? The answer is you need both, working together. The Problem VMware snapshots are great for quick rollbacks, but they create redo logs that strain storage IO and need eventual consolidation. During active snapshots, your storage reads multiple files simultaneously, potentially impacting production. Storage snapshots like Pure's are instantaneous and lightweight, but they capture entire volumes at once, are only crash-consistent, and require full restores or manual workarounds to extract specific data. Neither alone covers every recovery scenario you'll face. The Solution Integrate VMware, Pure Storage, and Veeam into a cohesive platform: Leverage Pure snapshots for fast, efficient data capture without production impact Use Veeam to orchestrate application-consistent backups and enable granular restores Keep snapshots close to the source for quick recovery Maintain backup files for long-term retention Replicate everything to DR sites with the same capabilities The Payoff One integrated solution gives you flexibility for any situation: ransomware recovery from immutable snapshots, granular file restores, site failovers, or long-term archive retrieval. All without impacting production. Modern data protection isn't about picking sides. It's about making your storage, hypervisor, and backup solution work together intelligently. Hear more here on Pure360 Pure Storage and Veeam- Why Architecture Matters512Views3likes1CommentTop 10 Reasons to Love Purity 6.9
(Because 6.7 is so 2024) 10. 🏋️♂️ Long-Life Release means it’s supported until June 2028 — which is about three years longer than that gym membership you swore you’d use. 9. 🌐 Works with all the latest FlashArray platforms, AWS, Azure… pretty much everything except your toaster (for now). 8. 🕵️♂️ Security updates so strong, even your data will feel like it’s in the witness protection program. 7. 🚀 Turn on File Services without downtime or approval from Pure product management — finally, a software update you don’t have to schedule for “that one weekend in Q4 when no one’s looking.” 6. 🙌 Encourages Self-Service Upgrades. Translation: fewer support tickets, more “Look, Mom, I did it myself!” moments. 5. 🔑 Default password warning. Yes, “pureuser” is adorable… until it becomes a resume-generating event. 4. 🍍 VMware improvements so good, your virtual machines just sent a fruit basket. 3. 🎛️ Fusion, Fusion, Fusion! Which is like having a universal remote for your data… without the panic of losing it between the couch cushions. 2. 📜 REST API 2.x release notes so thorough, they make War and Peace look like a sticky note. 🏆 You get to tell your boss you're on a "Long-Life Release," which sounds much more impressive than "I'm not doing an upgrade for a while." Check out the release notes for more! https://support.purestorage.com/bundle/m_flasharray_release/page/FlashArray/FlashArray_Release/01_Purity_FA_Release_Notes/topics/concept/c_purityfa_69x_release_notes.html978Views3likes0Comments
Active Cluster for File
Hello everyone :-) I'm new to Active Cluster for File and I'm looking for some documentation or introductory material. I'd like to understand: How Active Cluster for File works How it is configured via the management interface General setup, requirements, and administration tasks If anyone can point me to official documentation, knowledge base articles, or deployment guides, I would really appreciate it. Thanks!Solved325Views2likes7Comments🧠 Deep Dive: Configuring File Services Policies & File Systems on FlashArray
Continuing our technical walkthrough series on Pure Storage FlashArray File Services, this new video dives into the nuts and bolts of setting up policies and file systems to create your first SMB file share. If you’ve already followed along with the previous video on setting up networking, DNS, and Active Directory integration, this next step completes the foundation — showing exactly how to configure: Export Policies for SMB access and permissions Quota Policies to manage capacity limits Audit and AutoDir Policies for visibility and governance And finally, how to create and assign a file system for your department or team shares The demo walks through the FlashArray UI and even steps into Windows file share management to validate access-based enumeration and permissions in action — proving just how simple and powerful FlashArray file services can be. 👉 Watch the video on Pure360 to see how easy it is to go from blank configuration to a fully functional SMB file share environment in minutes. -Jason1.2KViews2likes1CommentA Platform for the Future
So, I’ve been at Pure Storage for a few seasons now. Hint: when I joined, the “//M” generation of FlashArray was still a little wet behind the ears, and was then styled as a lowercase “//m” (bonus points if you can guess the year I joined in your reply!). One of the things that has always impressed me the most about Pure, is how purposeful and thoughtful our development and engineering teams are. Most of us here had realized for years that Pure isn’t a collection of disparate products and features–it’s a real, integrated, intelligent storage platform! One OS (Purity). One flash architecture (DirectFlash). A universal NDU architecture, both software and hardware (Evergreen). Last year, we launched the Pure Storage Platform to make that engineering vision official. Today's announcements mark another huge milestone in the evolution of the Pure Storage Platform. We’ve unified operations across distributed infrastructures, maximized efficiency for AI, and embedded cyber resilience at every layer. Our engineers have outdone themselves once again. It all works together, so your organization can master its data, while you get more done. Pure Storage is helping enterprises turn data into a true business advantage. From edge to core to cloud, the message is clear: data should be unified, efficient, and resilient — so organizations like yours can innovate without compromise. Find out more about what we announced today in our blog. And let us know what you think below!166Views2likes0Comments