Node Navigation
Get Started Here
Featured Content
Start Here
Getting Started: 5 Steps to Get the Most Out of the Everpure Customer Community
2 MIN READ Welcome! You've taken the first step and created an account here. What to do next you ask? Here's five simple steps to take after registering to ensure you're getting the most out of this community...bmcdougallPlace User BlogsUser BlogsCommunity Manager3.3KViews20likes9Comments
Recent Discussions
Finding a Hidden SafeMode Gap in Under a Minute with Fusion MCP and Claude
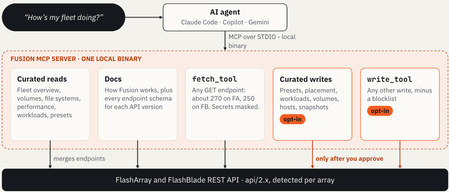
Slides are a poor way to show what a platform can do. A live problem, solved while the customer watches, shows it much better. An Everpure SE recently ran a Fusion enablement call with a customer who had been trying to track down a SafeMode misconfiguration on one of their arrays. They had looked but couldn’t find it. Partway through the session, the SE connected Claude to the customer’s environment through the Pure Fusion MCP server. Instead of clicking through array settings one at a time, the SE asked questions about the fleet in plain language and had Claude review the SafeMode configuration across it. Within a minute, the team had the answer: Per-object SafeMode wasn’t enabled on that array. What is Per-object SafeMode? SafeMode is Pure’s immutable snapshot protection, built to keep ransomware or a compromised admin account from destroying your recovery points. An intruder can’t set snapshot retention to zero and eradicate everything, and retention can only be shortened through Pure Support, with identity confirmed first. SafeMode started as an array-wide setting: all or nothing. Per-object SafeMode (also called Object-level SafeMode, or Per Protection Group SafeMode in earlier material) lets you enable it on specific protection groups instead, so you can focus protection on your most critical volumes. It works through the protection group’s retention lock: Unlocked: anyone with access can lower the snapshot schedule, shorten retention, or disable it. Ratcheted: retention can only go up. Lowering or degrading it requires Pure Support. SafeMode also comes in two newer forms: Default Protection SafeMode sets a default protection group for an array container, so any new volume inherits its snapshot and retention policies. Auto-On SafeMode turns protection on by default for new arrays, with no setup required. Why a gap here is easy to miss Because protection can be set per protection group, it can differ from group to group and from array to array. A snapshot schedule can look healthy while the retention lock behind it is still unlocked. That’s hard to spot when you’re checking arrays one at a time, and it matters most when someone with stolen credentials is trying to delete your snapshots. Why it matters A real data-protection gap, closed. SafeMode is a core part of a ransomware resilience strategy, and a misconfiguration there is exactly what you want to catch before an incident. Finding it strengthened the customer’s security posture right away. Fleet-wide visibility, shown rather than told. Fusion gives you one control plane across your arrays. Adding an AI assistant on top means you can ask a question about the whole fleet and get a fast, direct answer instead of auditing array by array. A better conversation. The call started as a standard feature walkthrough. Once the gap turned up, it became a real problem solved on the spot, and the customer responded very positively to the integration. The takeaway Configuration drift is easy to miss, especially across many arrays with per-group protection settings. Pairing Fusion’s single control plane with Claude through MCP turned a problem the team couldn’t find into a one-minute answer. If you’re curious how this could work in your environment, reach out to your Everpure team and we can walk through it live.5Views0likes0CommentsPurity//FA 6.5.14 LLR is here!
We are happy to announce the general availability of the 6.5.14 Long-Life Release, the fifteenth and final release in the 6.4/6.5 line: addresses improvements around controller failover and shutdown, S3 Offload restores, and DirectFlash firmware updates to improve service uptime, better manage restores, and enhance I/O performance. See the release notes for more details about what is included in this release.1View0likes0CommentsUpcoming Webinar: Inside Fiserv’s Kubernetes Platform
Fiserv runs containerized applications on a Kubernetes platform at scale across cloud and on-premises environments, hosting in-house applications and vendor software. The platform enables Fiserv to effectively deliver critical financial services to their customers. In this session, John Durko, Director of IT, Product Architect and Container Services, and Joselito Angeles, Principal Containers Platform Architect, share how their team uses Portworx to protect data, bring new features and services to market more quickly and simplify operations within their Kubernetes platform. Join us to learn: How Fiserv uses Portworx for immutable backups to keep recovery data tamper-proof in a highly regulated industry How self-service storage and data management for developers enable faster and more reliable deployments How Fiserv is extending one data layer from AKS to Red Hat OpenShift, and Amazon EKS. Register for the session here.5Views1like0CommentsOld Tech Tuesday: Holiday Catalogs
Hello Window Shoppers! Today we're going to talk about one of the things that seems to have gone away: catalogs. Sears, Radio Shack, Toys R Us, Circuit City. I recall flipping through those, window shopping, marking for your parents (or maybe Santa). The Sega Game Gear was featured in a few movies. It had the ability to control the future, which at the price is a relative bargain. What's the first item that comes to mind that you circled in a catalog, regardless of whether or not you got it?20Views0likes6CommentsRunning VCF on Everpure? Help shape an independent report, and receive a thank-you gift.
We're working with Omdia's Enterprise Strategy Group (ESG) on a new independent analysis of what it really costs to run VCF on external storage versus vSAN, for block and file workloads, including VDI. The goal is to show how Everpure enhances VCF environments. We want to show situations where VCF with Everpure adds significant, measurable value. The results will help other customers see how they can enhance and modernize their own VCF estate. We're looking for a few customers for a short interview, which Omdia will conduct and follow up on directly. Participation is anonymous. Neither you nor your company will be named in the report. Your contact details are shared only with Omdia to schedule your interview and will not appear in the report. Who we're looking for: Teams running VCF with Everpure storage for block, file, or both. You only need one. File use cases (NFS, SMB, user profile data) are a big plus. Willing to share your numbers in a short interview. A plus: you evaluated or moved from vSAN, or can share the vSAN configuration or quote you compared against. What Omdia will ask about (high level): Your environment: your VCF setup, and whether you run block, file, or VDI on Everpure. Costs: storage and server hardware, software and VCF licensing, and support. Savings: server reduction, plus power, cooling, and floor space. Administration: time spent managing storage, before and after. Comparison: what you evaluated or would have chosen instead, such as vSAN. Every participant receives a gift of Everpure swag. Interested? Comment below or message Heather Fedele at [email protected].9Views1like0CommentsTaking a moment of gratitude: What’s your must-have product capability? 🍽️✨
As we approach the end of the year, we’re pausing to celebrate everything that makes this community special, as well as the everyday ways you use Everpure products in your day-to-day workflow. If our products were a meal, what would be on your plate? 🌟 The Main Course: The single feature your daily workflow can’t live without. 🥖 The Side Dishes The quiet, reliable tool that keeps everything moving smoothly. 🍰 The New Favorite Dessert: A feature or update released this year that you immediately enjoyed. Tell us your top picks below and, if you feel so inclined, shout out a community member you appreciate! All participants will receive a thank-you gift from us!Old Tech Tuesday: Thanksgiving Double Feature
Hello friends, With Thanksgiving around the corner here in the US, we're doing a double feature this week: a little nostalgia and a little gratitude. 1. The Kid's Table: What's something that was the center of a gathering for the kids? Maybe it was a stack of VHS tapes, a Nintendo, Battleship, that Commodore 64. 2. Tech We're Thankful For: Memories Before memories could be captured on demand with your phone, moments had to be captured on other devices. What was your go-to piece of technology?Active Cluster For File Documentation?
Hello everyone :) Is there a documentation about Active Cluster for File? I haven't found one yet. What I have found was the link below and the video, where Quinn does a work through. https://support.everpuredata.com/r/activecluster/activecluster-file-quick-start-guide A step by step guide how to navigate and create NFS shares and so on in the Active Cluster for File Management Console would be handy. Thank you, in advanced!22Views0likes2CommentsFusion preset driven backup SLA
Using presets as the policy source of truth across vCenter and Veeam Sharing a pattern I have been running in my lab: using an Everpure Fusion preset as the single policy source that drives storage provisioning, vCenter placement, and backup SLA in one motion. The idea started from a simple frustration. We already encode a lot of intent into a Fusion preset: the array and pod, the protection group, snapshot schedule, replication, QoS. Then we throw most of that context away the moment the volume becomes a datastore, and a human re-decides protection downstream in a different tool. I wanted the preset to stay the contract all the way through, so provisioning once gets consistent storage and the right data protection without a second decision. The flow: I ask for a datastore of a given size from a named preset. Fusion deploys the volume with the preset’s protection group and settings. Provisioning mounts it, formats VMFS, and exposes it in vSphere, with a pre-flight check across the cluster hosts and a placement recommendation pulled from the fleet before any write. I assign the datastore a tier, which lands as a vCenter tag. That tag is what the backup vendor keys off (Veeam here), so the SLA follows the storage. What stood out from a Pure angle: The preset as source of truth. I can clone the protection group at provisioning time, change snapshot frequency or replication per workload, and the downstream tag and backup follow. The preset is not just a storage shortcut, it is the policy definition, and everything else derives from it. Fleet-wide placement. Rather than guessing which array has room, the recommendation came from the fleet: the target array reported 4% used with host visibility confirmed up front. At fleet scale this is the difference between consistent tiering and a pile of one-off decisions that drift apart array to array. Immutability that lines up across layers. SafeMode and Object Lock on the array pair naturally with an immutable backup repository on the other side, so the higher tiers get immutability at both the primary and the backup copy. For a ransomware conversation, being able to say tier 1 is immutable on the array and in the backup, by policy, not by hope, is the whole point. The governance angle is what I think matters most. When the preset defines the tier and the tier is enforced automatically downstream, “tier 1” means the same thing on every array and for every workload. You stop relying on the operator to remember what tier 1 is supposed to look like this week. I orchestrated it with MCP servers (Fusion, vCenter, Veeam) so every change is gated behind an approval, and it caught a real conflict mid-run, a protection-group name collision, and offered cleanup versus redeploy instead of failing. It even flagged the root cause (the protection group name is built from the first 25 characters of the workload name) so future builds avoid it. But the Fusion mechanics underneath are standard presets; the orchestration is just what made it conversational and safe. Full write-up with architecture and screenshots: https://thebetasociety.com/wcith/pure-storage/everpure-mcp-policy-from-preset-to-veeam-backup/ Video walkthrough: https://youtu.be/FAVeVXPJECo How it Works: https://beta-society-site.pages.dev/wcith/pure-storage/everpure-mcp-policy-to-backup-how-it-works Would love to hear how others are using presets as a policy layer, especially anyone tying Fusion presets to downstream systems like backup, CMDB, or showback.33Views0likes0CommentsPortworx Backup 3.2.0 is now GA
Hello Everyone, Portworx Backup 3.2.0 is now Generally Available! This release expands VM protection with support for SUSE Virtualization, file and folder restore for Windows Server VMs, and per-VM restore outcomes. It also adds IPv6 and dual-stack networking in Classic mode and a single view for managing backup schedules across clusters. Key features SUSE Virtualization support: Portworx Backup now supports backing up and restoring VMs running on SUSE Virtualization clusters. File and folder restore for Windows Server VMs: Restore selected files or folders from a backup to the same KubeVirt VM running 64-bit Windows Server, without restoring the entire VM. This extends the existing Linux VM capability to Windows Server. It requires Stork 26.5.0 or later and the QEMU Guest Agent installed and running on the VM. Partial Success for VM restores: Multi-VM restores now report the outcome of each VM separately. If some VMs restore successfully while others fail, the restore completes with Partial Success and the successfully restored VMs remain available. This capability applies to Classic mode and requires Portworx Enterprise 3.7.2 or later and Stork 26.5.0 or later. IPv6 and dual-stack networking: Classic mode now supports IPv6-only and dual-stack networking on OpenShift and vanilla Kubernetes. Configure the cluster networking before installing or upgrading Portworx Backup. Fleet-wide backup schedule management: A new Backup schedules page brings schedules across clusters into one view. Operators can filter schedules, suspend or resume them, and delete schedules individually or in bulk. Filtered views can be shared or bookmarked. Available in both Classic and Federated modes. MongoDB master encryption key rotation: Replace the MongoDB master encryption key during an upgrade. The pre-upgrade health check reports whether the new key was applied or the existing key was retained. These are the highlights. Portworx Backup 3.2.0 also includes Helm 4.x support for supported deployments, VM snapshot cleanup and restore troubleshooting improvements, console usability updates, and fixes. See the release notes for the full list and upgrade considerations. License Server UI change: Portworx Central is retiring Lighthouse and discontinuing its monitoring service. As part of this change, Portworx Backup 3.2.0 decouples the License Server UI from Portworx Backup and Portworx Central. Manage Portworx Enterprise licenses through a standalone License Server or lsctl. Portworx Backup licensing is unchanged. Continue to manage those licenses from the License page in the PX-Backup console. Documentation and Resources Portworx Backup - Release Notes (3.2.0): Portworx Backup Release Notes Portworx Backup - How to Upgrade: Upgrade Portworx Backup (Classic) and Upgrade Portworx Backup (Federated) Portworx Backup - Requirements: Pre-requirements Portworx Backup - Docs: Portworx Backup Documentation On behalf of the Portworx Backup Team, Vijay Nagarajan12Views2likes0Comments
Upcoming Events
- Nov19Thursday, Nov 19, 2026, 09:00 AM PST
- Nov25Wednesday, Nov 25, 2026, 12:00 PM GMT
- Dec3Thursday, Dec 03, 2026, 09:00 AM PST
Featured Places
Introductions
Welcome! Please introduce yourself to the Pure Storage Community.Pure User Groups
Explore groups and meetups near you./CODE
The Everpure /Code community is where collaboration thrives and everyone, from beginners taking their first steps to experts honing their craft, comes together to learn, share, and grow. In this inclusive space, find support, inspiration, and opportunities to elevate your automation, scripting, and coding skills, no matter your starting point or career position. The goal is to break barriers, solve challenges, and most of all, learn from each other.Career Growth
A forum to discuss career growth and skill development for technology professionals.
Featured Content
As we approach the end of the year, we’re pausing to celebrate everything that makes this community special, as well as the everyday ways you use Everpure products in your day-to-day workflow.
If ...
1 day ago11Views
0likes
0Comments
If your current process for "just snapshot that volume before the change window" involves a browser tab, an SSH session, maybe a semi-remembered purevol flag, and a Slack message that starts with "he...
6 days ago198Views
4likes
0Comments
Want to get a head start on your holiday shopping? Share your honest, firsthand Everpure experience to receive gift cards you can use now: Gartner Peer Insights (GPI) will send you a $25 gift card f...
7 days ago41Views
1like
0Comments
Hey everyone!
As more organizations evaluate open-source virtualization, we’ve formally joined forces with Proxmox under the Everpure Technology Alliance Partner program. We’ve listened to your fee...
12 days ago230Views
4likes
0Comments
Hello everyone :-) we recently got a Flasharray with the new "ActiveCluster for File" feature, which is pretty nice. We are trying to switch to Veeam. We are using VMware. I therfore created a...
29 days ago216Views
1like
8Comments